3 engagements
Plus technical due diligence
How we work with you
Three ways to work with us, each led by Daryn, who answers for the outcome. Technical due diligence is also available as a one-off review.
6 to 12 months
Monthly fee, in a written proposal
Fractional CTO
For a health company with engineers or a delivery partner but no senior technical lead. The board wants one person who answers for the platform, and the founders want their time back.
What you get
A senior technical lead for around 8 days a month, working alongside your team and accountable for what ships.
- One roadmap that product, engineering and the board work from
- Delivery partners tracked against agreed scope, quality and dates
- Security and compliance evidence ready before a health system or investor asks for it
How it starts
After a first conversation you get a written proposal, with the scope, days a month, monthly fee, term and notice period.
In the first 2 weeks we meet the people who build, run and pay for the platform, and get read access to the code, cloud accounts, tickets and incident history.
In weeks 3 and 4 we review the architecture, the codebase, delivery and security against what the business needs next.
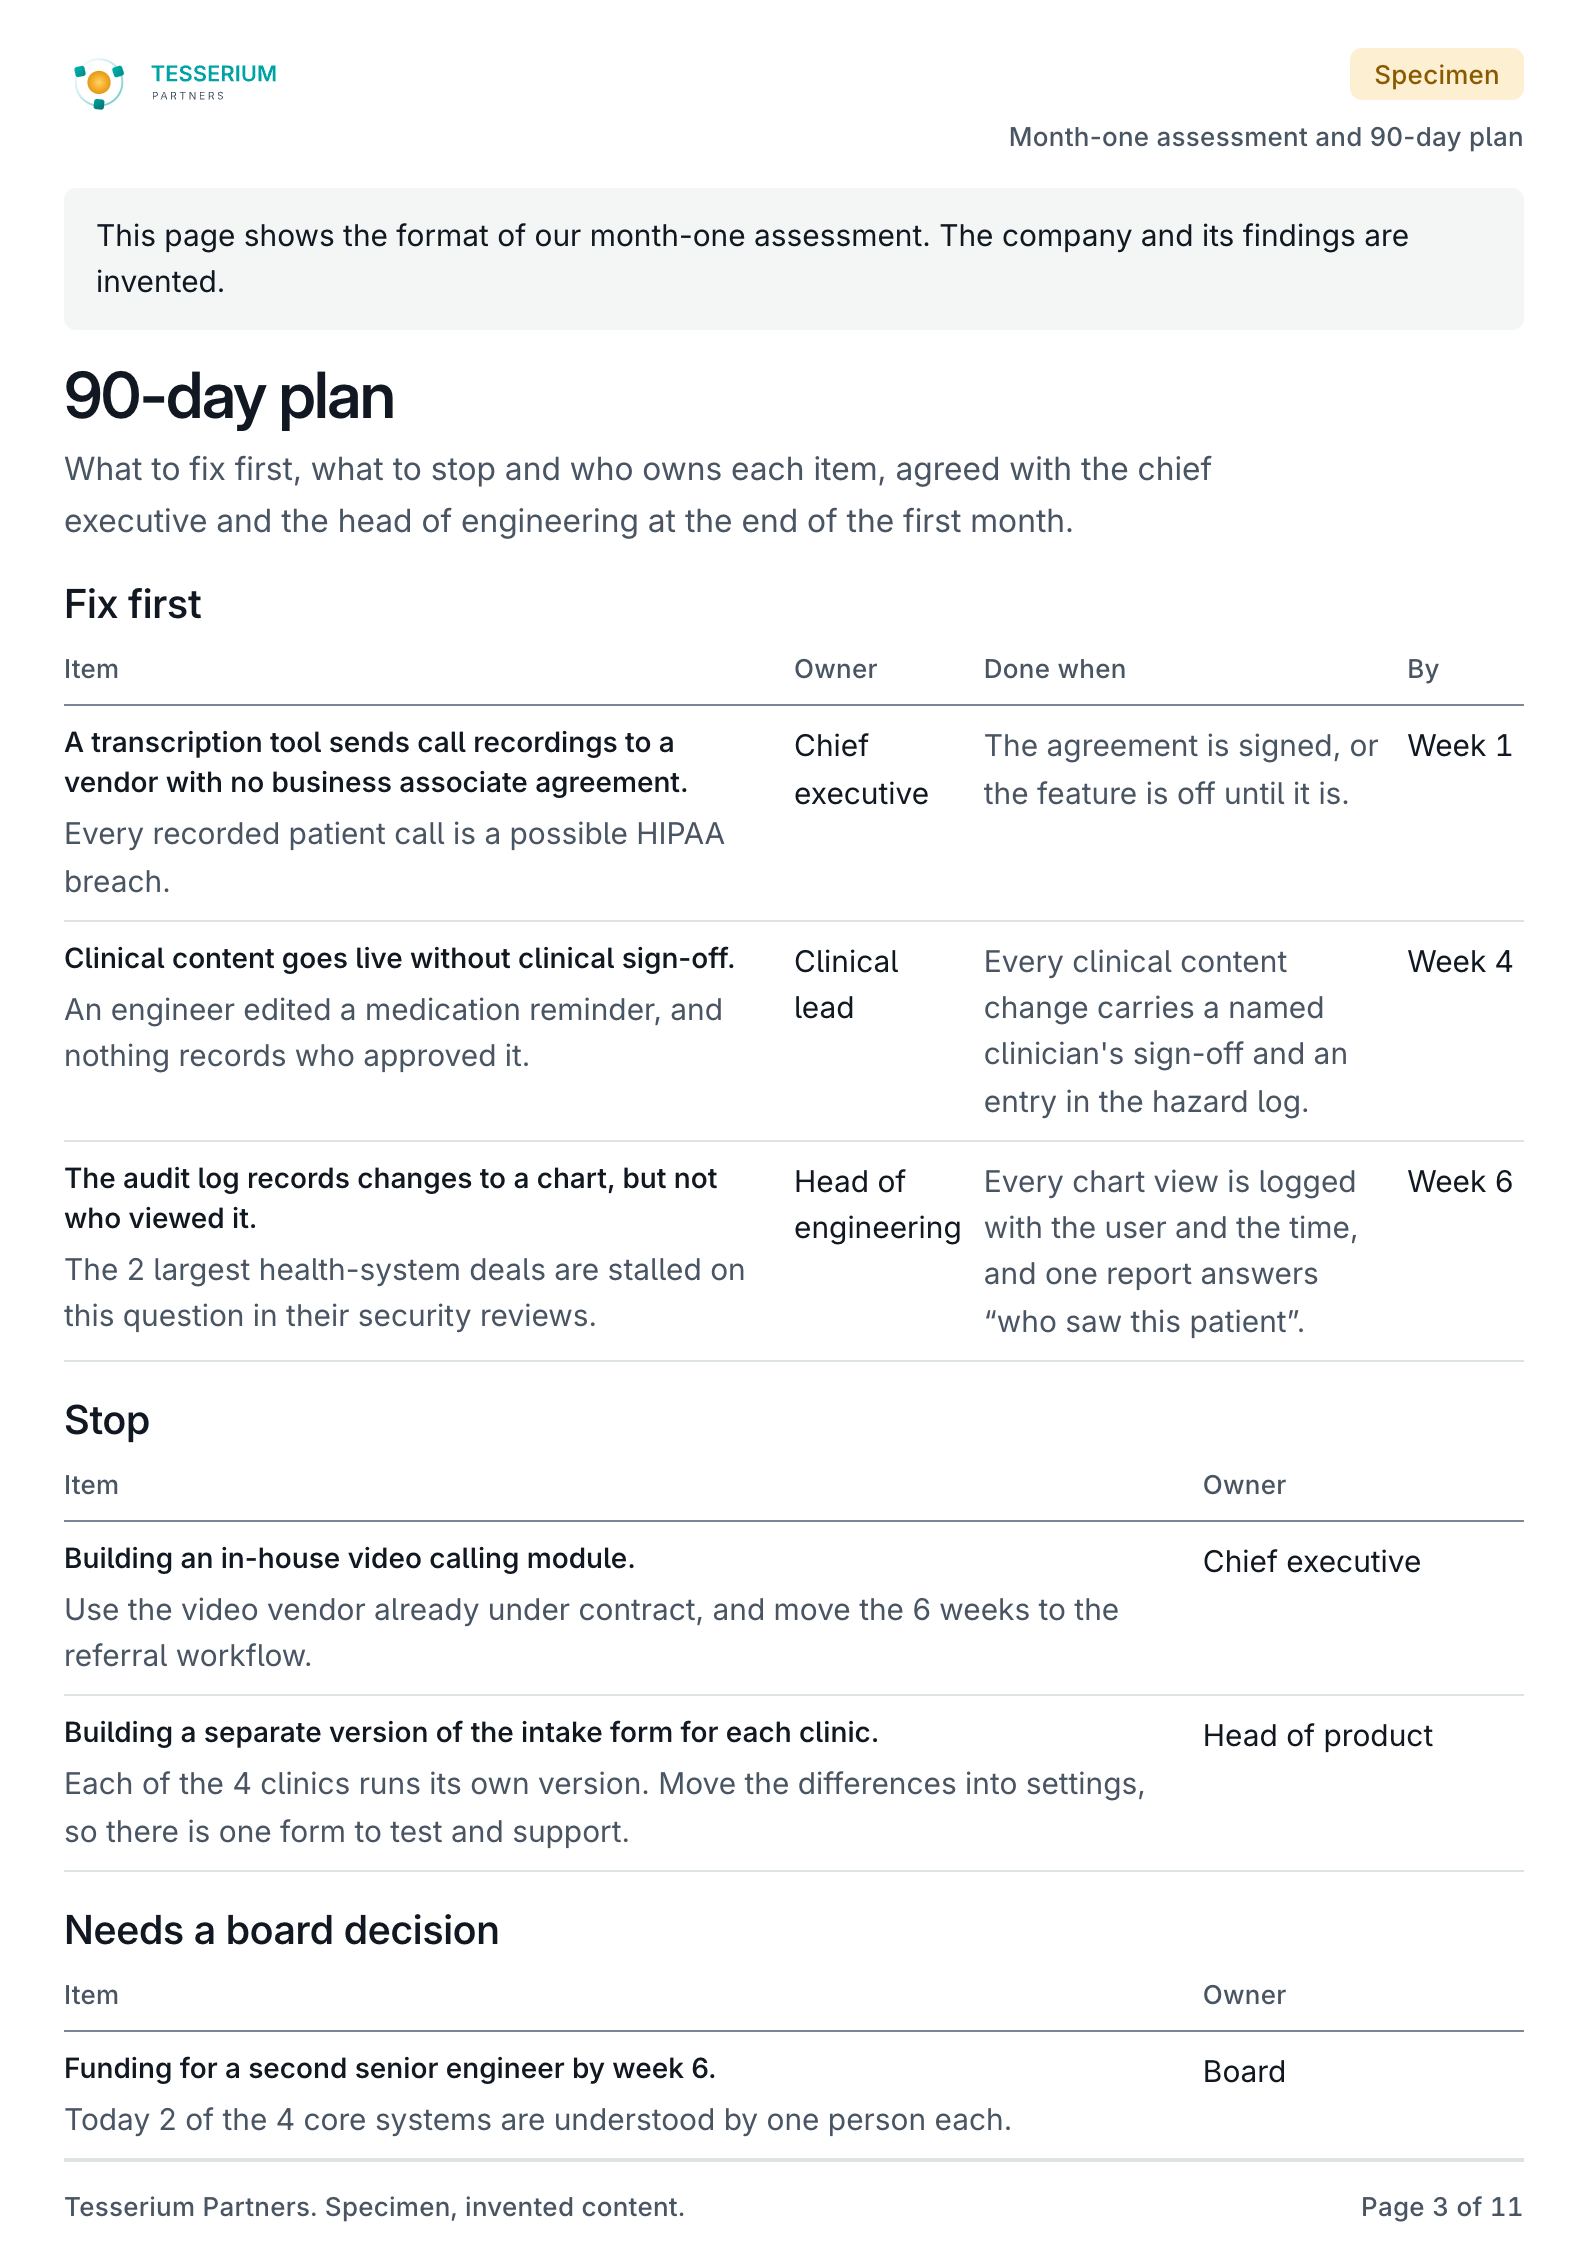
By the end of the first month you have a written assessment and a 90-day plan, with what to fix first, what to stop and who owns each item. From then on we work to that plan, and the board gets a written update each month.
90 days
Fixed fee, in a statement of work
90-day sprint
For one problem with a date on it, such as an audit finding to close, a module to ship or a certification to prepare for, with a team ready to take it on afterwards.
What you get
One defined piece of work with an agreed outcome, sized to fit 90 days.
- An outcome agreed in writing and measured against week 1
- A written update every week against that outcome
- A team ready to run the work without us
How it starts
A scoping session, then a statement of work with the outcome, how we will both know it is met, what is out of scope, a fixed fee and the access we need.
In week 1 we measure the starting point, so every report shows progress against it, and confirm the milestones with you.
Every week you get a written update against the outcome. Any change to the scope is agreed in writing before work on it starts.
The last 2 weeks are handover to your team, with the documentation, a walkthrough and 2 to 4 weeks of support afterwards.
3 months minimum
Monthly fee, in a written proposal
Advisory
For founders, boards and investors who need a senior technical view every month without a hire. It suits a company between technical leads, or a board that wants an independent read on what its engineering team reports.
What you get
A senior technical view each month, independent of your team and your vendors.
- A second opinion on what the engineering team reports to the board
- Architecture choices reviewed against what the business needs
- Vendor and build-or-buy decisions tested against your own requirements
How it starts
An intake call and a read of your board pack, roadmap and architecture documents.
The first session sets the questions for the quarter.
Each session runs for 2 hours and is followed by a written note of decisions and actions. Between sessions you can email questions, answered within 2 working days.
For a single investment or acquisition, technical due diligence needs no advisory minimum.
One-off
Fixed fee, agreed before work starts
Technical due diligence
A one-off review of a health company's technology before you invest in it or buy it. A fixed fee, agreed before work starts, with no ongoing commitment.
Who it is for
For investors and acquirers, and for founders who want to know what a buyer's review will find before it starts.
What we look at
- The architecture, the code and the technical debt, and what it would cost to fix
- Security and data protection, against what a health system's reviewers will ask for: HIPAA in the US, UK GDPR and the NHS Data Security and Protection Toolkit in the UK, and OWASP for the code
- Clinical safety and medical device status: which rules apply (the MHRA or FDA for devices, DCB0129 for clinical safety in England) and what evidence exists
- Billing and claims logic, where revenue depends on it
- Cloud costs, and how they grow with customers
- AI features: how they are built, tested and governed
- The team, the delivery process and the risk if one person leaves
- Who owns the code, open-source licences and what the platform depends on
- How credible the roadmap is with the team and budget behind it
How it works
A call to agree the questions that matter for the deal, then a fixed-fee proposal.
Read-only access to the code, cloud accounts and documents, and interviews with the technical lead and key engineers. We do not need patient data, and we sign a business associate or data processing agreement before any access that could reach it.
A written report with red flags first, each finding rated, the cost and time to put it right, and questions to put to management.
A call to walk you through it, and an outline of the first 100 days after the deal.
A red flag review covers only what could change the deal and takes about a week. A full review takes 2 to 4 weeks from the day we have access.
Independence and reliance
We do not review a company we advise, one that competes with a client, or one that competes with a business Daryn runs.
We sign your non-disclosure agreement before we see deal material.
Before each review we declare in writing any interest Tesserium or Daryn has in the company, its competitors or the deal, including other directorships. If any could affect our view, we decline the work.
Our fee is fixed before work starts and does not depend on the deal going ahead. We take no referral or finder's fee from anyone.
For 12 months after a review we take no work from the company we reviewed, unless the party that commissioned the review asks us to.
The report is addressed to whoever commissions it. Anyone else relies on it only through a signed reliance letter. It is a technical opinion, not an audit, a penetration test or a legal opinion on who owns the code.
How we take work
What you can expect from us, and the work we turn down.
We do
- Lead product and engineering for health software where a billing rule, a clinical workflow or a security control has to be right.
- Take on a few clients at a time, so the person who answers your enquiry is the person who does the work.
- Agree the scope and the outcome in writing before work starts.
- Leave written decisions and a handover your own team can run without us.
We don't
- Supply contractors to fill seats in your team.
- Make clinical decisions. Clinical content and sign-off stay with your clinicians.
- Take a fee or commission from a vendor we recommend.
8 questions
Before you get in touch
Answers to what people ask before an intro call.
Who will do the work?
Daryn does. He leads every engagement and does the senior technical work himself. Where code needs writing, we lead your developers or your delivery partner. If the work needs a specialist, such as a penetration tester, we name them in the proposal and you meet them before they start.
You are in the UK. Can you work with a US organisation?
Yes. Daryn has led product and engineering for US value-based care organisations for 6 years, and our clients today are in the US. We sign business associate agreements, work to the HIPAA rules that apply to a business associate, and to CMS billing rules where a client asks for them. We invoice in US dollars.
Will you sign a business associate agreement?
Yes, at least five business days before any access that could reach patient data. In the UK, we sign a data processing agreement.
When can we talk?
Calls run 2pm to 6pm UK time, which is 9am to 1pm US Eastern time for most of the year. When we reply, we suggest times.
How long do engagements last?
A fractional CTO engagement usually runs 6 to 12 months, at around 8 days a month. A sprint runs 90 days on a fixed scope. Advisory runs for at least 3 months. Technical due diligence is a one-off review.
How do you handle conflicts of interest and intellectual property?
We keep each client's work apart from other clients and from our own products. We tell you about any possible conflict before you sign, and the contract sets out who owns what before work starts.
What does it cost?
A sprint or due diligence review is a fixed fee, agreed before work starts. A fractional CTO or advisory engagement is a monthly fee for agreed days or sessions. The price depends on the days, the term and the size of the platform. Invoices are payable within 15 days. We do not publish prices.
Company number 16868098
For procurement and security teams
The short answers. A supplier pack with the detail is available on request.
- Company
- Tesserium Partners Ltd, registered in England and Wales, company number 16868098. Registered with the Information Commissioner's Office, C1958700. Not VAT registered.
- Certification
- Tesserium holds no security certification of its own. We build client work to the standards listed under Standards we work with on the Home page, and can show the working behind each.
- Insurance
- Professional indemnity with technology errors and omissions, cyber, public liability, employers' liability, and directors' and officers' insurance. Certificates and limits on request.
- Patient data
- We work without patient data wherever we can. Where our access could reach it, we sign a business associate agreement in the US or a data processing agreement in the UK first.
- Access
- We work from the UK, on encrypted devices with multi-factor sign-in, and where you prefer, through accounts you create and can remove. Evidence on request.
- AI tools
- We tell you which AI tools we use on your work and on what terms, and we keep patient data out of them. You can object to any tool before we use it.
- Security incidents
- We tell you about a security incident affecting your data without undue delay, and always within the time your contract sets (48 hours under our standard data processing agreement).
- Security contact
- Report a suspected security issue in our website or our work to security@tesserium.co.uk.
- Specialists
- Specialists sign terms at least as strict as ours.
- Ownership
- What we produce is yours once the invoice is paid.
- End of engagement
- We hand back or delete your data, apart from records the law requires us to keep, and confirm in writing that our access is removed.
- Payment
- Invoices in pounds or US dollars, payable within 15 days of the invoice date. Form W-8BEN-E for US clients.